

Linn Maung
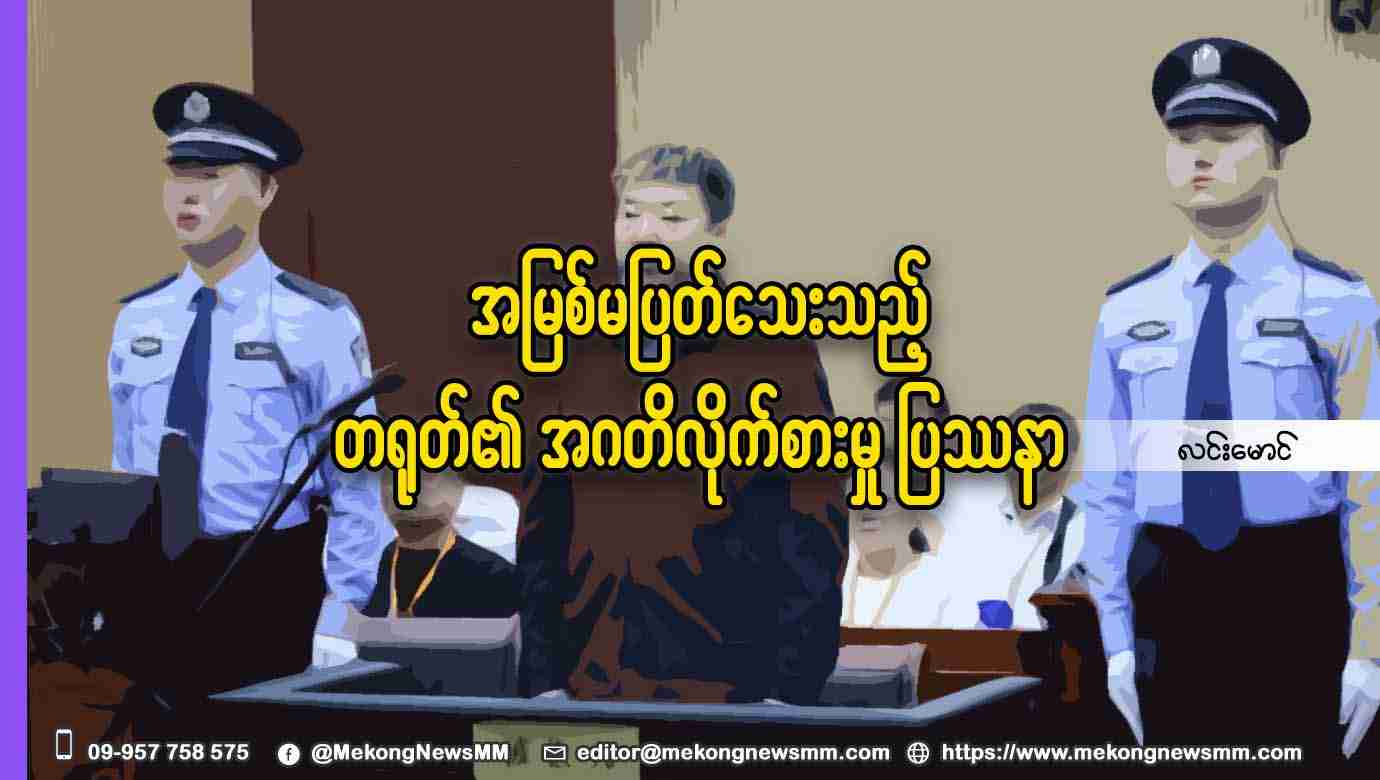
Government-linked Chinese hackers have intensified their cyber attacks on Taiwanese research centers, particularly those affiliated with the government and specializing in computing and technology. One notable incident occurred in July 2023, when a hacking group believed to be part of the state-sponsored APT41 infiltrated a Taiwanese research center. The attackers used malware typically associated with China-based groups to steal passwords and sensitive documents.
According to cyber security experts, the hackers exploited vulnerabilities in outdated software, such as an older version of Microsoft Office, to gain access to the research center’s systems. This breach lasted for 11 days, during which the attackers managed to ex-filtrate a significant amount of data. The attack highlights the persistent and sophisticated nature of cyber threats posed by Chinese state-sponsored groups, which have been increasingly targeting Taiwanese organizations amid escalating geopolitical tensions.
The Chinese government has consistently denied any involvement in such cyber attacks, labelling accusations as “groundless smears”. However, cyber security experts warn that these cyber espionage activities are part of China’s broader strategy to assert its geopolitical aims and undermine Taiwan’s security and technological advancements. The ongoing cyber threats underscore the need for robust cyber security measures and international cooperation to counteract these sophisticated attacks.
A cyber security firm has reported that a suspected China-backed hacking group has ramped up its attacks on organizations in Taiwan, as part of Beijing’s intelligence-gathering efforts on the self-governing island.
The hacking group, known as Red Juliett, infiltrated around two dozen organizations between November 2023 and April 2024. This activity is believed to support intelligence collection on Taiwan’s diplomatic relations and technological advancements, according to a report released on Monday by Recorded Future.
Red Juliett exploited weaknesses in internet-facing devices, such as firewalls and Virtual Private Networks (VPNs), to breach its targets. These targets included tech companies, government bodies, and universities, as stated by the U.S.-based cyber security firm. Additionally, Red Juliett conducted “network reconnaissance or attempted exploitation” against over 70 Taiwanese organizations, including several de facto embassies, the firm reported.
Recorded Future’s report reveals that Red Juliett has been highly aggressive in targeting Taiwan’s technology sector, focusing on critical technology areas. The group conducted vulnerability scans and attempted to exploit a semiconductor company and two aerospace firms with military contracts. Additionally, Red Juliett targeted eight electronics manufacturers, two technology-focused universities, an industrial embedded systems company, a technology research and development institute, and seven computing industry associations. This extensive targeting underscores Red Juliett’s intent to gather intelligence on Taiwan’s technological advancements and its strategic industries.
While nearly two-thirds of Red Juliett’s targets were in Taiwan, the group also compromised organizations in other regions. These included religious organizations in Taiwan, Hong Kong, and South Korea, as well as a university in Djibouti. Recorded Future anticipates that Chinese state-sponsored hackers will persist in targeting Taiwan for intelligence-gathering activities. The cyber security firm expects these groups to continue focusing on reconnaissance and exploiting public-facing devices, a tactic that has proven effective in gaining initial access to a wide range of global targets. This method allows hackers to infiltrate various sectors, from technology to academia, and gather valuable intelligence. Chinese Foreign Ministry spokeswoman Mao Ning stated she was unaware of the report and dismissed Recorded Future as not credible, highlighting the ongoing tension and scepticism between China and cyber security firms reporting on state-sponsored hacking activities. “We also anticipate that Chinese state-spon
sored groups will continue to focus on conducting reconnaissance against and exploiting public-facing devices, as this has proved a successful tactic in scaling initial access against a wide range of global targets,” the cyber security firm said. Chinese Foreign Ministry spokeswoman Mao Ning told reporters she was not aware of the report, but that Recorded Future was not a credible organisation.“The company you referred to has a history of spreading false information about alleged ‘Chinese hacking operations.’ Their work lacks both professionalism and credibility,” she stated.
China has consistently denied involvement in cyber-espionage, a practice that many governments engage in. Instead, Beijing portrays itself as a frequent target of cyber attacks. Additionally, China asserts that Taiwan, a democratically governed island, is part of its territory, despite never having controlled it.
Tensions between Beijing and Taipei have escalated as Taiwan’s Democratic Progressive Party aims to elevate the island’s international standing. On Monday, Taiwanese President William Lai Ching-te criticized Beijing for issuing legal guidelines that threaten the death penalty for advocates of Taiwanese independence.“I want to emphasize that democracy is not a crime; autocracy is the true evil,” Lai told reporters. Branded a “separatist” by Beijing, Lai maintains that there is no need to formally declare Taiwan’s independence, as it is already a sovereign state.
#MeKongNews